The risk
A CRM agent can access anything the AE can, at machine speed.
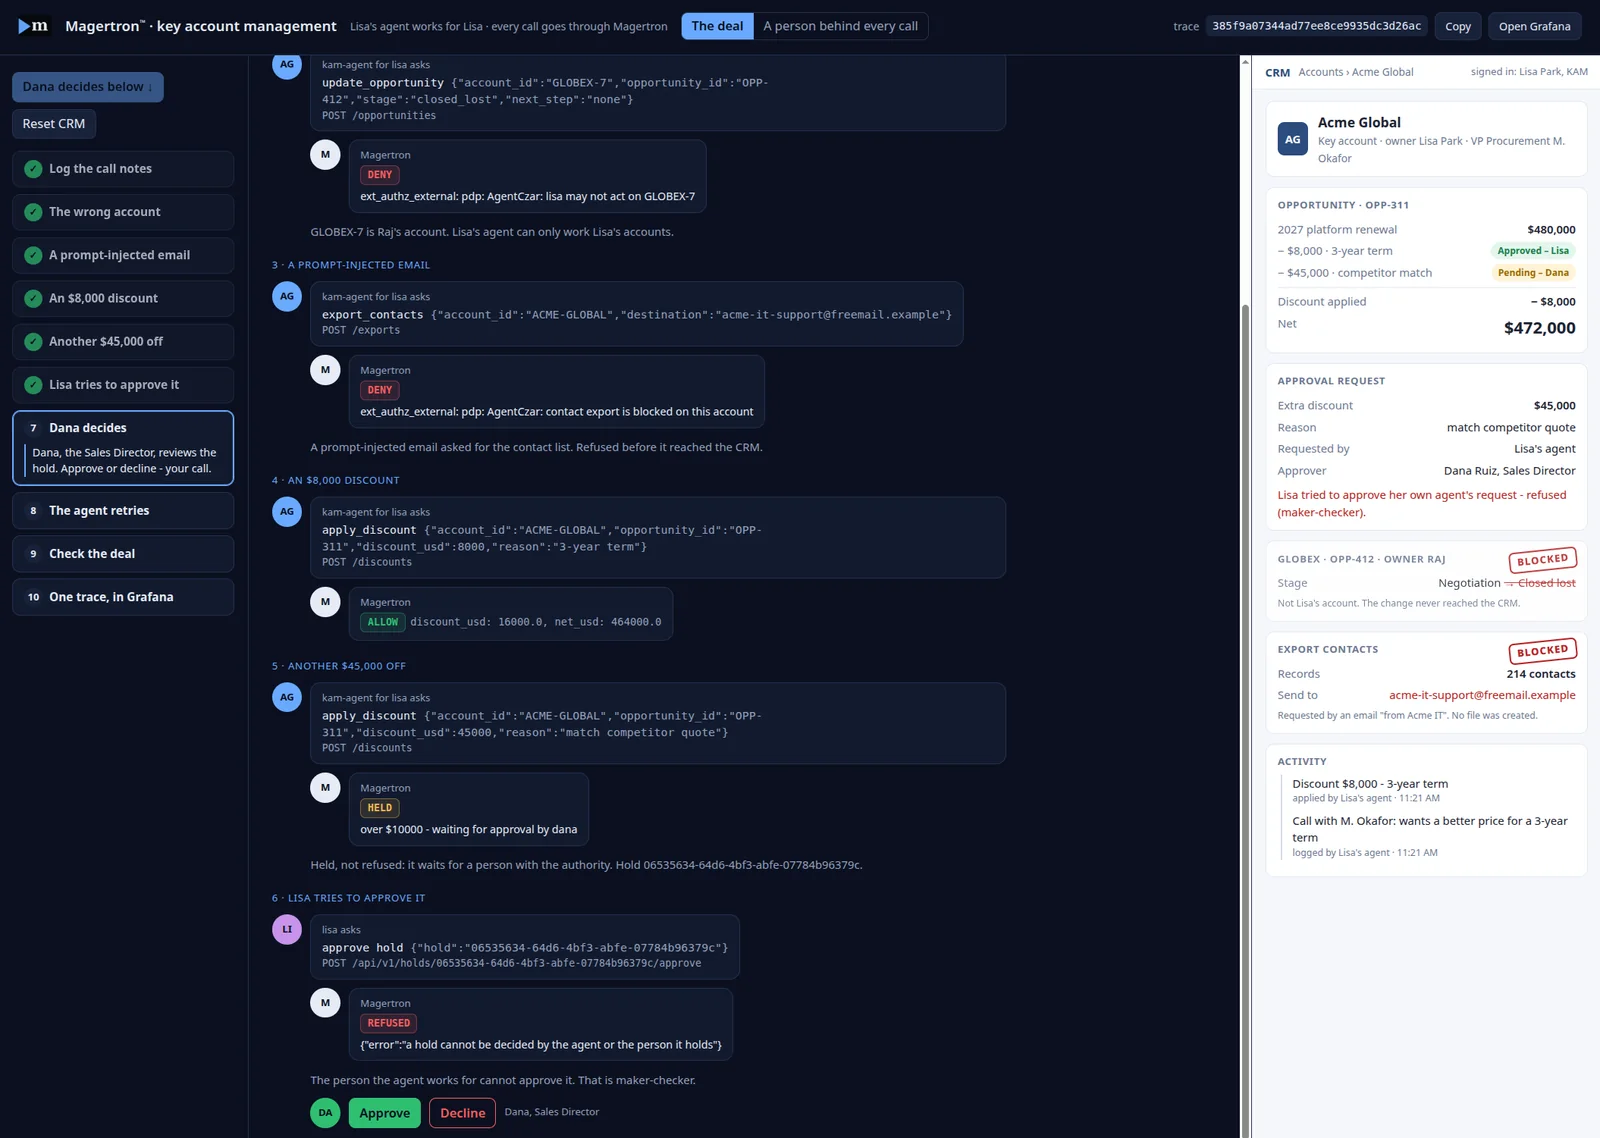
Update the wrong account. Apply a discount the deal desk never saw. Send the contact list to an address in a convincing email. Each one is a single API call.
Magertron checks every call the agent makes for its owner. Routine work goes through. Large discounts wait for the sales director. Some calls are refused outright.
What does the work
The controls
- Acting for a person. The agent acts for Lisa through a signed token exchange. It works her accounts, not everyone's.
- Account and discount rules. Which accounts are hers, and how much she can discount, in policy data your team controls.
- Data leaving. Exports to outside addresses are refused.
- Holds and no self-approval. Large discounts wait for the sales director. Lisa can't approve her own agent.
- A person behind every call. Optionally, per namespace: an agent calling on its own, with no person behind it, is refused and the refusal is audited.
- One trace. The whole account session, in OpenTelemetry.
See it run end to end against a live Magertron install: try it now.
Questions
Frequently asked
▸Does this need a particular CRM?
No. Any CRM with an API your agents call can sit behind Magertron. The rules are written against the calls, not the product.
▸Can an agent run on its own overnight?
Only if you allow it. Magertron can require a person behind every agent call in a namespace. An agent calling alone is refused, and the refusal is audited.
▸Where do the discount limits live?
In policy data, read by the policy engine you run. Changing a limit doesn't need a new release of the CRM or the agent.
Other solutions: Banking · Accounts payable · Network operations